What Is Phishing?

Phishing is a scam where someone impersonates a trusted sender, such as a bank, a coworker, or a well-known company, to trick you into handing over credentials, payment details, or other sensitive information. It usually arrives as an email, text message, or fake website designed to look convincing enough that you act before you stop to question it.
The goal is almost always the same: get you to click a link, open an attachment, or type in information you would never hand to a stranger. Phishing works because it targets trust and urgency rather than technical weaknesses, which is why it remains one of the most common ways accounts and systems get compromised.
How a phishing attack works
A typical phishing attempt starts with a message crafted to look like it comes from someone you already trust. It might mimic a bank’s login alert, a shipping notice, or an internal email from a manager. The message usually creates a reason to act quickly, such as a security warning, an overdue invoice, or a locked account.
The link inside points to a fake page built to resemble the real login screen for that service. Anything typed there, a username, a password, a card number, goes straight to the attacker instead of the legitimate company. Some versions skip the fake site entirely and ask you to reply with information or call a number the attacker controls.
Common phishing variants
Phishing takes several forms depending on the channel and the target.
- Spear phishing targets a specific person or role, using details gathered about them to make the message feel personal and credible.
- Smishing uses text messages instead of email, often pretending to be a delivery service, a bank, or a two-factor authentication code request.
- Business email compromise involves an attacker impersonating an executive or vendor to request a wire transfer or a change to payment details.
- Vishing uses a phone call, where the attacker poses as support staff or a bank representative to extract information verbally.
Each variant relies on the same underlying trick: borrowing the appearance of a trusted relationship to lower your guard.
Warning signs to watch for
Most phishing attempts share a handful of traits once you know what to look for. A sense of urgency, a request to verify an account immediately, or a threat of suspension is a common opener. The sender’s actual email address often does not match the organization it claims to represent, even when the display name looks right.
Links can be checked before clicking by hovering over them to see the real destination, which frequently points to a domain that only loosely resembles the real one. Generic greetings, unexpected attachments, and requests for information a legitimate company would never ask for over email are all reasons to pause.
Why phishing matters
A single successful phishing attempt can expose a password that unlocks far more than one account, especially when that password gets reused elsewhere. For businesses, a compromised employee inbox can lead to fraudulent payments, stolen customer data, or an attacker gaining a foothold to move further into internal systems.
Phishing does not require breaking encryption or exploiting a software flaw. It targets people directly, which is part of why it continues to work even as other technical defenses improve.
How to start defending against it
Turning on multi-factor authentication is one of the most effective steps available, since a stolen password alone is no longer enough to access the account. Pausing before clicking a link in an unexpected message, and typing a known web address directly instead, avoids most fake login pages entirely.
A password manager helps too, since it will not autofill credentials on a lookalike domain the way a person might mistake for the real one. For teams, regular awareness training combined with email filtering that flags suspicious senders reduces how many attempts ever reach an inbox in the first place.
Machines are patient enough to try endless variations, but my taste is what finally tells me the search is over.
Itamar Haim
Where Sticklight fits
Sticklight is the vibe-coding platform built for professional web creators, and the sites, apps, and dashboards people build with it are exactly the kind of destination phishing pages try to impersonate. You describe what you want to build in plain language, and Sticklight turns that prompt into a production-ready website, app, dashboard, CMS, or tool, with the underlying setup that keeps real user logins and data handled properly from the start.
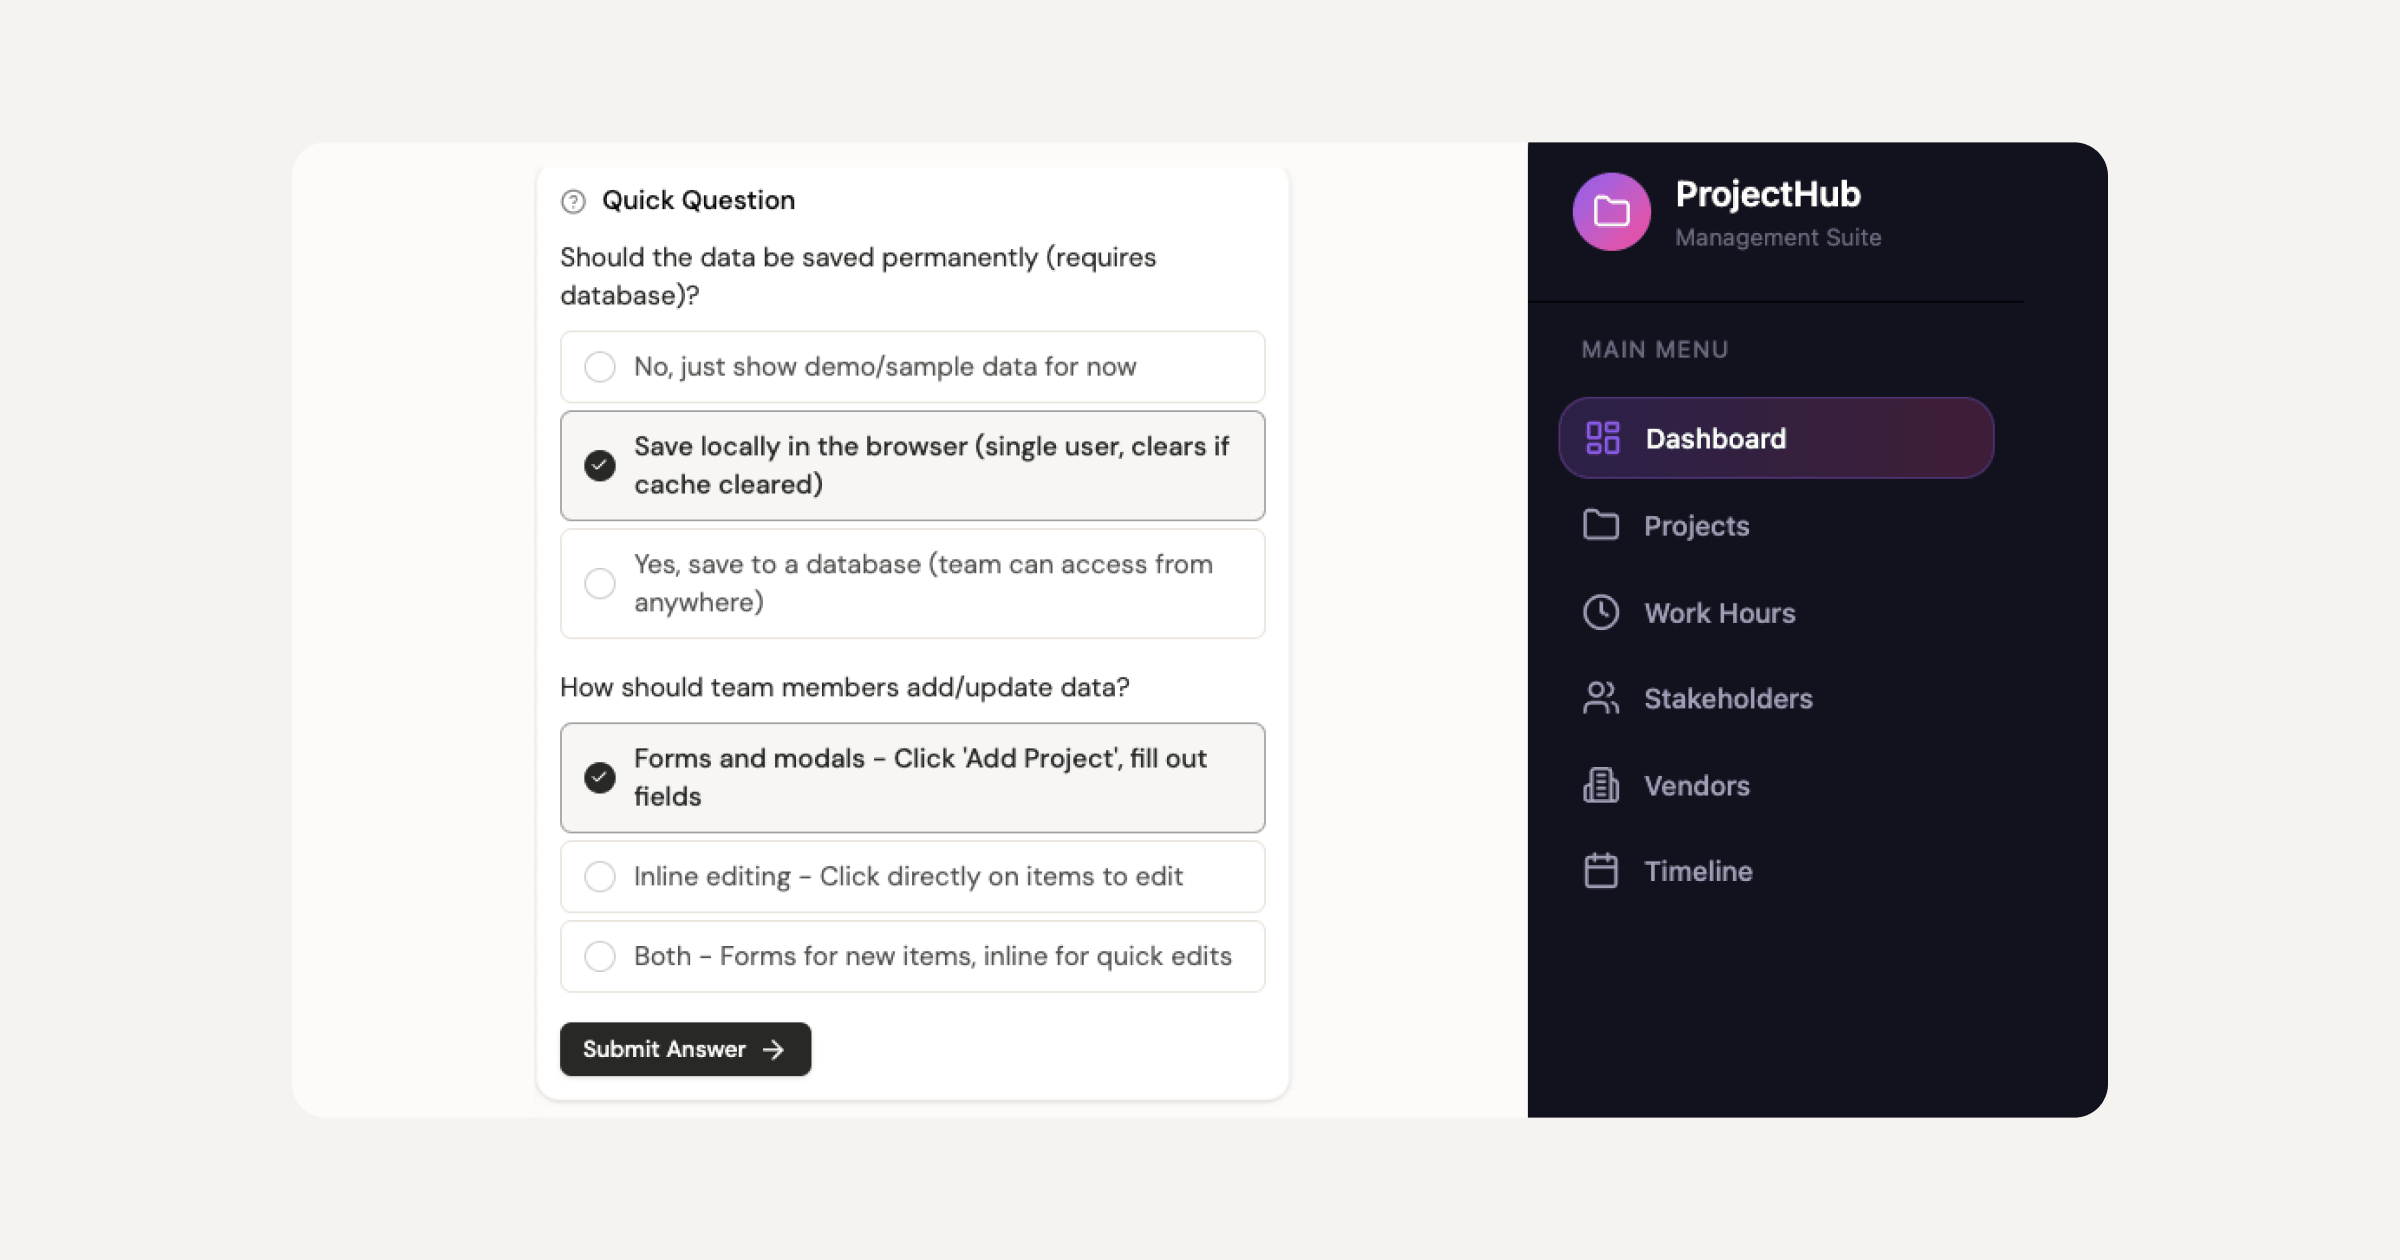
That includes the groundwork behind account creation, authentication, and data storage, so a creator is not left guessing how to protect user credentials as a project grows. Sticklight is built to go beyond simple websites toward being a full-stack creator’s workspace, covering backend and infrastructure concerns as well as the interface.
WordPress and Elementor remain part of that picture too. Sticklight extends what you can already do with them, giving creators who know that ecosystem a way to add modern, prompt-driven capability on top of it rather than replacing what already works.
Frequently asked questions
What is the main goal of a phishing attack?
The main goal is to trick someone into handing over sensitive information, such as a password, a credit card number, or account access, by impersonating a source the target already trusts.
How can I tell a phishing email from a real one?
Look for a mismatched sender address, a generic greeting, urgent or threatening language, and links that point to a domain that only resembles the real company’s site when you hover over them.
What is the difference between phishing and spear phishing?
Phishing is sent broadly to many people with a generic message, while spear phishing is tailored to a specific person using personal or organizational details to appear more credible.
Is smishing the same thing as phishing?
Smishing is a form of phishing carried out over text message rather than email, often impersonating a delivery service, a bank, or a login verification code.
What should I do if I already clicked a phishing link?
Change the password for that account right away, enable multi-factor authentication if it is not already on, and check the account for any activity you do not recognize.
Built by the Elementor team. Powered by Claude.
Let it glow.