What Is Two-Factor Authentication?

Two-factor authentication, often shortened to 2FA, is a login method that requires two different, independent pieces of proof before granting access to an account: something you know, like a password, plus a second factor from a separate category. That second factor comes from a different kind of proof than your password, so someone who steals your password alone still cannot get in.
The reasoning is simple. A single secret is easy to lose control of, through a data breach, a phishing page, or a password reused across sites. Pairing it with a second, unrelated factor closes that gap, since an attacker now needs to compromise two separate things instead of one.
The three factor categories.
Security professionals sort login proof into three categories, and understanding them explains why 2FA works the way it does.
- Knowledge: something you know, like a password, PIN, or answer to a security question.
- Possession: something you have, like a phone, a hardware security key, or a smart card.
- Inherence: something you are, like a fingerprint, a face scan, or another biometric trait.
Real two-factor authentication combines factors from two different categories. Entering a password and then a second password does not count, since both come from the knowledge category and both can be stolen the same way, say, through the same breach. Pairing a password with a code generated on your phone does count, because getting hold of one does not hand an attacker the other.
Common second factors you will run into.
Once you turn on 2FA for an account, you are usually asked to choose how you want to receive or generate that second factor.
- Authenticator apps, which generate a short numeric code that refreshes every 30 seconds, tied to a secret shared only between the app and the service when you set it up.
- SMS codes, texted to your phone number each time you log in.
- Hardware security keys, small physical devices you plug in or tap that confirm your identity through cryptographic proof rather than a code you type.
- Push notifications, sent to a trusted app on your phone that you approve with a tap.
Each option trades convenience for a different level of protection, which is worth knowing before you settle on one.
Why two-factor authentication matters.
Passwords get exposed more often than most people expect. They surface in data breaches, get guessed through automated tools, or get typed into a convincing fake login page. Once a password is out, anyone holding it can sign in as you on any account where that same password still works.
2FA changes that equation. Even if an attacker has your exact password, they still need your phone, your authenticator app, or your security key to finish logging in. That second requirement stops the large majority of automated and opportunistic attacks, since attackers working from a stolen password list rarely also have access to your device.
How to start using it.
Most major services, including email providers, banks, and social platforms, let you turn on 2FA from the account or security settings menu, often under a label like “two-step verification” or “login approvals.” Setup typically asks you to scan a QR code with an authenticator app or confirm a phone number, then walks you through a test login to confirm everything works.
A good starting point is your email account, since it is often the recovery path into everything else you own. Whichever service you set up, save the backup codes it gives you somewhere safe, in case you ever lose access to your phone or key. Where a service offers a choice, an authenticator app or hardware key is a sturdier pick than SMS.
A note on phishing-resistant methods.
Not every second factor offers the same protection. SMS codes and app-generated codes are a real improvement over a password alone, but a convincing fake login page can still trick a person into typing that code into the wrong place, letting an attacker capture and reuse it within the code’s short window.
Hardware security keys and passkeys close that gap. They rely on cryptographic proof tied to the real website’s address, so even if you land on a lookalike page, the key simply will not respond, because it recognizes the address does not match. For any account where a break-in would cause real harm, a hardware key or passkey gives meaningfully stronger protection than a code you copy and paste.
I still get a small charge every time a sentence I typed becomes something a stranger could click through and actually use.
Itamar Haim
Where Sticklight fits
Sticklight is a vibe-coding platform built for professional web creators: you describe what you want in plain language, and it turns that prompt into a production-ready result, whether that is a website, an app, a dashboard, a small content system, or a working tool. Login flows and authentication logic, including support for a second factor, are the kind of underlying build work Sticklight handles as part of turning a prompt into a real, working product.
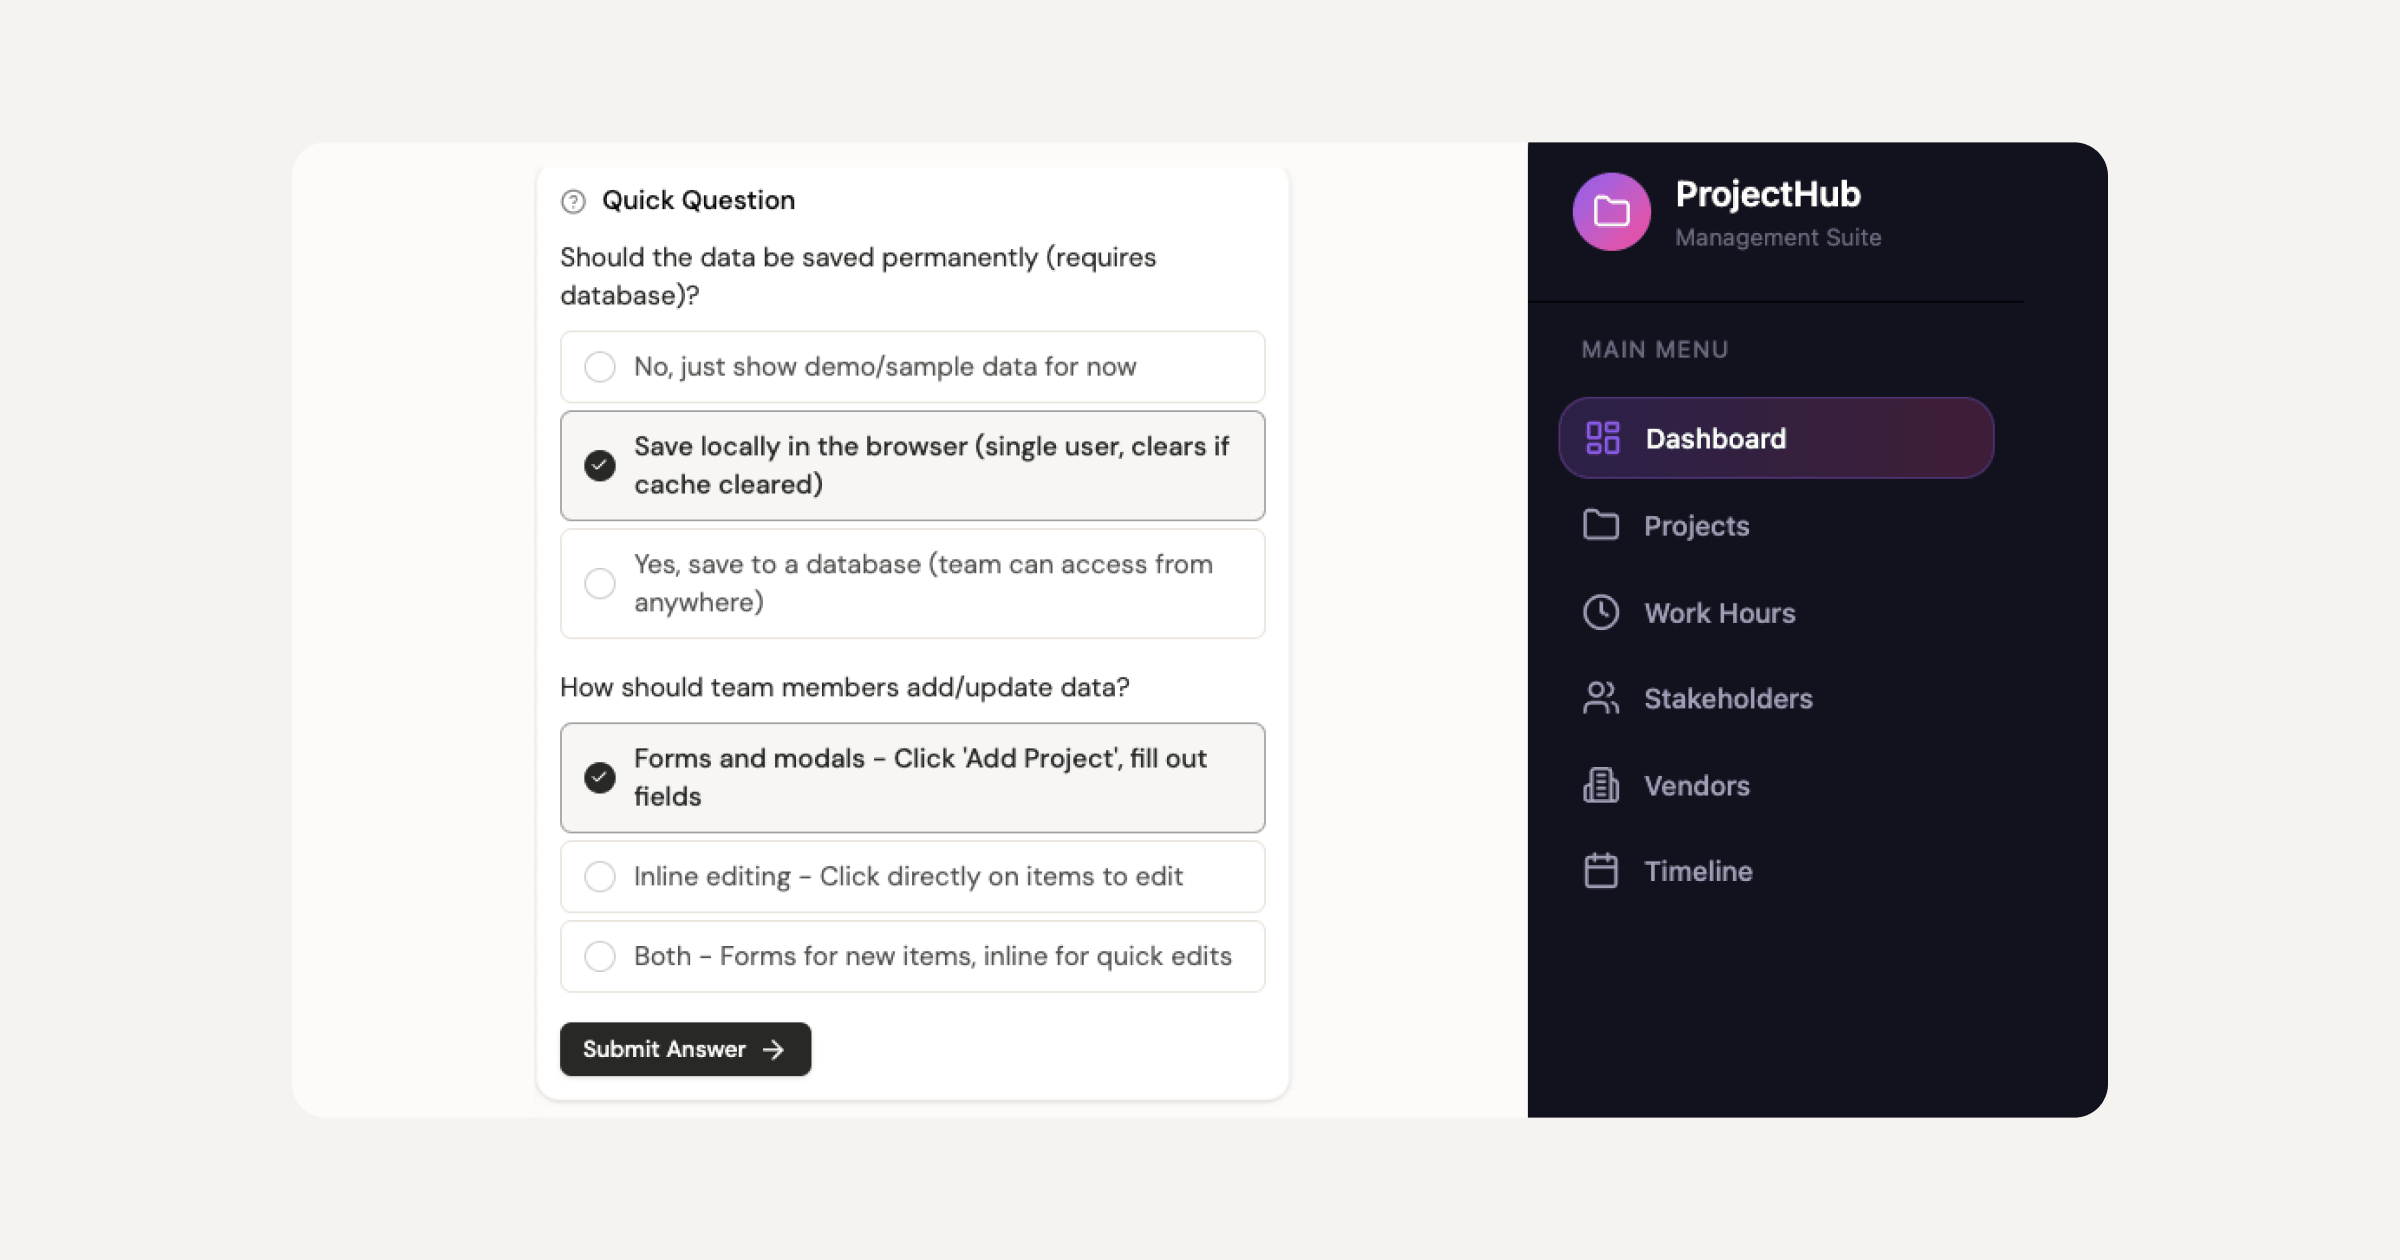
That range is the point. Sticklight is built to go beyond a single website and toward being a full-stack creator, covering ground that once needed separate tools and separate teams. WordPress and Elementor remain solid ways to extend what a site can do, and Sticklight adds a faster, prompt-first path alongside them for building everything from a landing page to a full application.
Frequently asked questions
What is two-factor authentication in simple terms?
Two-factor authentication, or 2FA, is a login method that requires a password plus a second, independent piece of proof, like a code from your phone, before granting access to an account.
Is a PIN plus a password considered two-factor authentication?
No, because a PIN and a password both come from the same knowledge category and can be stolen the same way. True 2FA pairs factors from two different categories, such as knowledge and possession.
Which second factor is the most secure option?
Hardware security keys and passkeys tend to offer the strongest protection, since they use cryptographic proof tied to the real website’s address and will not respond on a lookalike phishing page.
Is SMS-based two-factor authentication still worth using?
Yes, an SMS code is still a real improvement over a password alone, though it is more exposed to phishing than an authenticator app or a hardware key.
What should I do if I lose my phone after setting up 2FA?
Use the backup codes the service gave you during setup to regain access, then set up 2FA again on your new device and generate a fresh set of backup codes.
Built by the Elementor team. Powered by Claude.
Let it glow.